

Descriptions
Hands-On Web Exploitation Course, Learn practical web application security and bug bounty hunting through a hands-on course led by experienced security researchers Ben Sadeghipour (NahamSec) and Adam Langley. Develop your hacking methodology through real-world scenarios, practical exercises, and dedicated browser-based labs rather than relying solely on theory. The course covers security fundamentals, web application architecture, HTTP, proxy tools, regular expressions, reconnaissance, subdomain enumeration, JavaScript analysis, and fuzzing. Explore a wide range of web security vulnerabilities, including Cross-Site Scripting (XSS), Content Security Policy (CSP) bypasses, Cross-Site Request Forgery (CSRF), Cross-Origin Resource Sharing (CORS), PostMessage exploitation, open redirects, client-side path traversal, Local File Read (LFR), Insecure Direct Object References (IDOR), SQL injection, upload vulnerabilities, Server-Side Request Forgery (SSRF), XML External Entity (XXE), Remote Command Execution (RCE), JWT vulnerabilities, reverse proxy attack vectors, authentication vulnerabilities, account takeover techniques, and vulnerability chaining. Learn how to approach targets, analyze login pages, investigate potential weaknesses, and develop a structured reconnaissance and exploitation methodology. The course includes 24 modules, 170 lessons, more than 15 hours of video content, and 65 hands-on labs designed to mirror real bug bounty environments. Labs run in dedicated cloud infrastructure and are accessible directly through your browser, without requiring local virtual machines or a particular operating system. Learn from practical strategies and real-world insights from experienced bug bounty hunters, and optionally challenge yourself with an official practical certification exam featuring 10 realistic security challenges, dedicated testing infrastructure, unlimited retries, and a digital certificate signed by both instructors.
This course is designed to help learners develop practical web exploitation and bug bounty hunting skills, understand how vulnerabilities work, recognize potential attack vectors, and improve their ability to investigate and assess web application security. Training is delivered through realistic scenarios, guided demonstrations, hands-on practice, and a structured progression from foundational concepts to more advanced vulnerability discovery and exploitation techniques. The course also provides access to a learning community, ongoing course updates, and resources to support continued learning. No previous hacking experience is required; basic familiarity with how websites work is helpful but not mandatory. The training focuses on practical learning in dedicated educational lab environments and is intended to develop responsible security testing skills.
What you’ll learn
- Understand web security fundamentals, web application architecture, HTTP, and the essential tools used in practical web exploitation.
- Develop a structured reconnaissance methodology, including subdomain enumeration, JavaScript analysis, fuzzing, and target discovery.
- Understand and investigate common web application vulnerabilities, including XSS, CSRF, CORS, open redirects, IDOR, SQL injection, SSRF, XXE, RCE, and other security weaknesses.
- Learn how to analyze authentication systems, login pages, JWTs, reverse proxies, and account takeover attack vectors.
- Practice web exploitation techniques through guided demonstrations and 65 hands-on labs in dedicated browser-based environments.
- Improve vulnerability discovery, investigation, exploitation methodology, and vulnerability chaining through realistic bug bounty scenarios.
- Build practical skills through 24 modules, 170 lessons, and more than 15 hours of video training.
- Optionally prepare for the official practical certification exam by completing 10 realistic security challenges in dedicated testing infrastructure.
Who this course is for
- Beginners interested in ethical hacking, web application security, and getting started with bug bounty hunting.
- Aspiring bug bounty hunters who want to develop practical reconnaissance, vulnerability discovery, and web exploitation skills through hands-on labs.
- Security researchers, penetration testers, and cybersecurity learners seeking to expand their knowledge of common web vulnerabilities and real-world testing methodologies.
- Developers and IT professionals who want to better understand web application vulnerabilities, attack vectors, and practical security testing techniques.
Specificatoin of Hands-On Web Exploitation Course
- Publisher : HackingHub
- Teacher : Ben Sadeghipour
- Language : English
- Level : All Levels
- Duration : 15 hours and 15 minutes
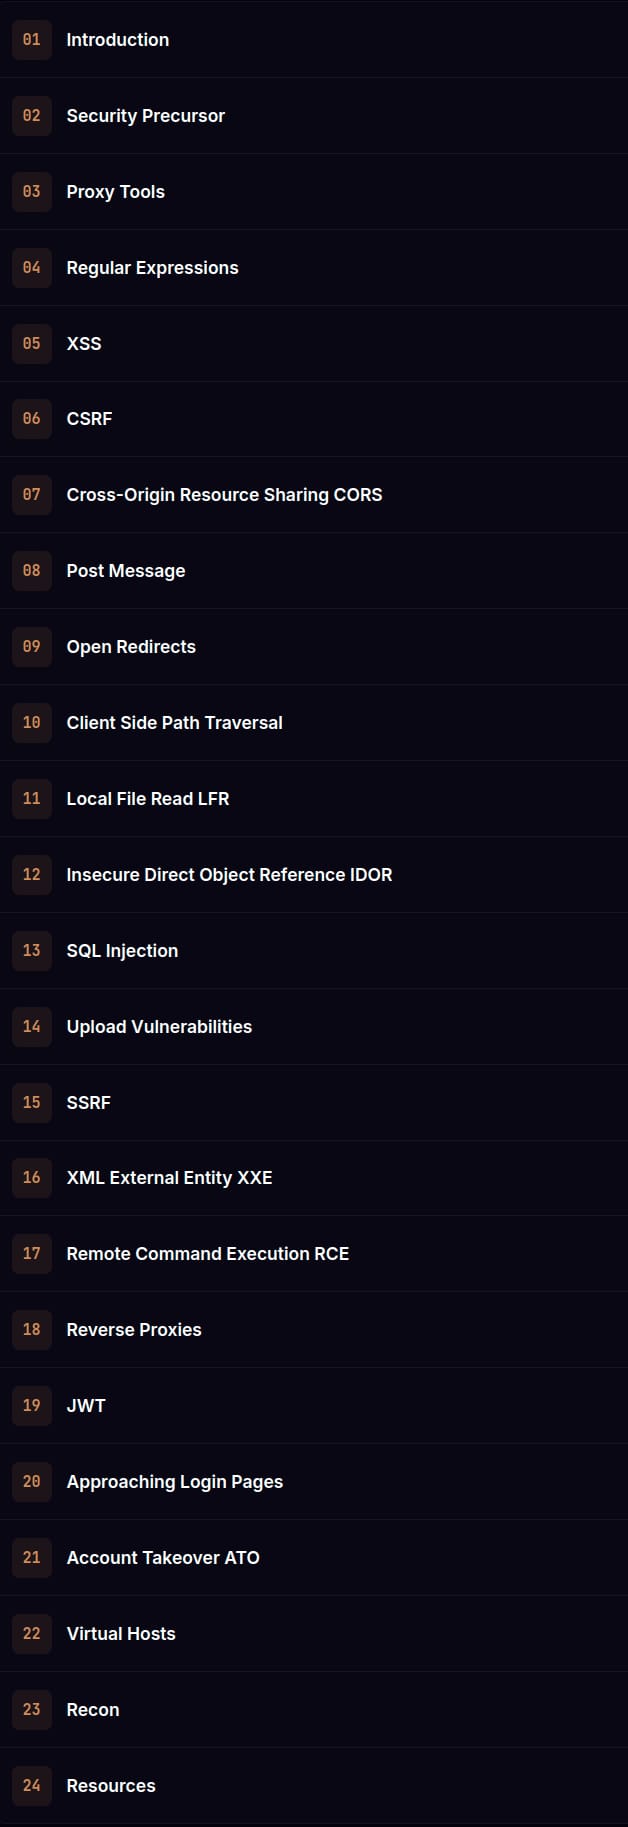
Content of Hands-On Web Exploitation Course
Pictures
Sample Clip
Installation Guide
Extract the files and watch with your favorite player
Subtitle : English
Quality: 720p
Download Links
Password file(s): www.downloadly.ir
File size
2.95 GB
2 Comments. Leave new
add rapidgator please
Hi
You can download from VIP servers only:
https://downloadlynet.ir/downloads/vip-membership