
Description
Attacking AI Applications. This course is a specialized and practical cybersecurity program that teaches how to identify, test, and compromise AI-based applications through architectural evaluation, command injection, and manipulation of data retrieval systems. This course is designed as a comprehensive and practical guide for cybersecurity professionals and penetration testers to learn how to evaluate and attack AI-based software. AI applications typically connect language models to documents, programming interfaces, user data, and business processes. While these extensive connections increase the efficiency of applications, they also create new attack vectors that traditional web testing tools and methods cannot uncover. This course teaches learners how to translate architectural blueprints of an AI application into practical and efficient penetration tests. During this course, participants will first learn to identify areas where command injection and restriction bypasses are most likely to occur using an attack surface map. Hackers will then perform direct and indirect command injection experiments and gain the ability to differentiate between generic security bypasses and real security vulnerabilities. In the final sections, they will learn how to manipulate additive manufacturing systems by retrieving them using techniques such as field padding, query routing, forced exit, and controlled poisoning scenarios via malicious documents. By the end of the course, learners will have the skills to discover weaknesses in AI applications, clearly demonstrate security implications, and provide professional reports.
What you will learn
- Converting the architectural blueprint of AI applications into practical tests to assess the attack surface
- Implementing direct and indirect command injection techniques and examining the impact of jailbreaking on systems
- Distinguishing generic security bypasses from real security vulnerabilities and threats
- Manipulation of information retrieval systems using field padding, query steering, and forced output techniques
- Implementing controlled poisoning scenarios using malicious source documents
- Professional reporting and clarification of security implications for presentation in real-world assessment projects
This course is suitable for people who:
- Penetration testers and cybersecurity assessors who want to develop their skills in the field of artificial intelligence
- Software security professionals who want to identify vulnerabilities in applications connected to language models
- Security researchers interested in investigating new vulnerabilities in AI systems
- Engineers and architects of artificial intelligence systems who want to make their applications more secure against attacks.
Attacking AI Applications course details
- Publisher: Pluralsight
- Instructor: Malek Mohammad
- Training level: Beginner
- Training duration: 1 hour and 31 minutes
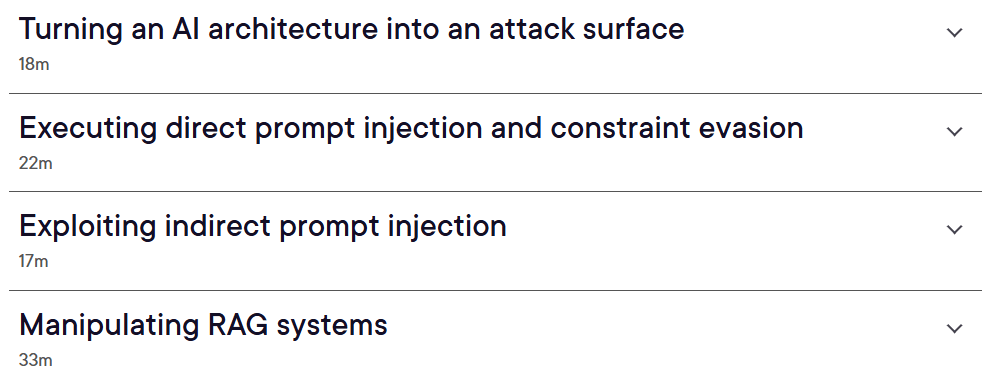
Course topics
Course images

Sample course video
Installation Guide
After Extract, view with your favorite player.
Subtitles: English
Quality: 1080p
Download link
Rapidgator link
File(s) password: www.downloadly.ir
File size
238 MB