
Description
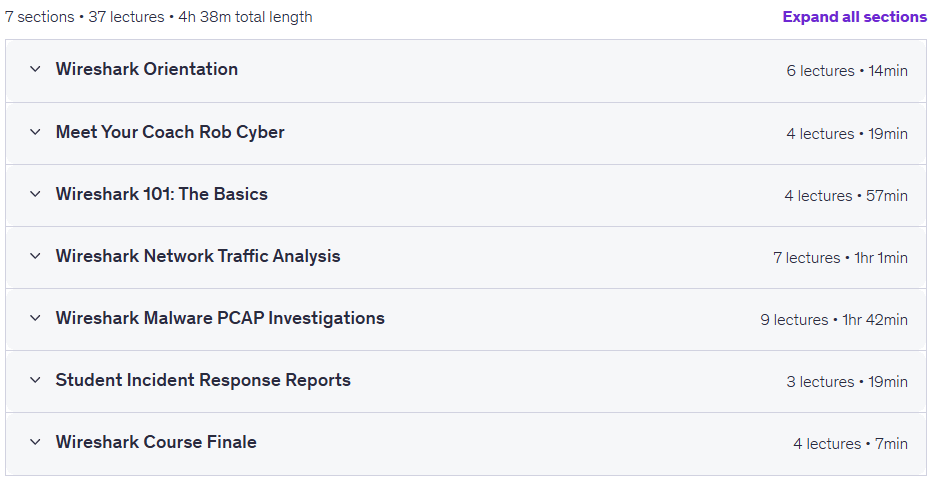
Wireshark for Cybersecurity: Malware PCAP Analysis. This course is a hands-on, hands-on program that teaches cybersecurity enthusiasts and security operations center analysts how to use Wireshark to analyze network traffic and examine files containing malware. This course is designed as a comprehensive, hands-on guide to teach participants key, real-world network traffic analysis skills. In today’s cybersecurity world, simply knowing how to open a PCAP file is not enough; hiring managers and employers are looking for people who have deep skills in analyzing suspicious network behavior, investigating malicious malware activity, and accurately documenting security research findings. This course helps learners move beyond filtering tools and theoretical jargon to encounter real-world network traffic, malicious code, and real-world scenarios. During this training program, participants learn how to identify suspicious activities such as port scans, brute force attacks, and ping flooding by examining various network protocols, server response codes, various connections, and encrypted traffic. A significant part of the course is also dedicated to the practical examination of PCAP files associated with known malware such as Darkgate, NetSupport, and Matanbochus. These examinations help learners track malicious communication patterns and document the discovered evidence using incident response reports. In addition, the course prepares individuals for specialized job interviews and provides skills that can be used to answer interviewers’ questions about network analysis, security incident response, and threat analysis methods, and to gain full preparation for entering the professional job market.
What you will learn
- Analyze PCAP files in Wireshark to identify suspicious network activity and support cybersecurity investigations
- Specialized examination of port scans, brute force attacks, ping flooding, and traffic from various protocols such as HTTP, FTP, SSH, and SQL
- Create professional incident response reports for recruiters and managers to accurately document evidence and findings from Wireshark investigations
- Fully prepare for Security Operations Center and Cybersecurity Analyst job interviews by learning how to explain research and answer technical questions.
This course is suitable for people who:
- Forward-thinking security operations center analysts who want to enhance their practical skills
- Enthusiasts and emerging professionals in the field of cybersecurity
- IT professionals looking to transition into cybersecurity
- Network help desk and technical support experts
- Network and systems administrators
- Students and individuals who want to add malware analysis with Wireshark to their skill set
Wireshark for Cybersecurity: Malware PCAP Analysis Course Details
- Publisher: Udemy
- Instructor: Rob Cyber
- Training level: Beginner to advanced
- Training duration: 4 hours and 38 minutes
- Number of lessons: 37
Course topics
Prerequisites for the Wireshark for Cybersecurity: Malware PCAP Analysis course
- No Experience Required. Go from ZERO to HERO
- Windows or MacOS Desktop or Laptop
Course images

Sample course video
Installation Guide
After Extract, view with your favorite player.
Subtitles: None
Quality: 1080p
Download link
Rapidgator link
File(s) password: www.downloadly.ir
File size
5.8 GB