
Descriptions
Linux Heap Exploitation – Part 1, For nearly 20 years, exploiting memory allocators has been something of an art form. Become part of that legacy with HeapLAB. The GNU C Library (GLIBC) is a fundamental component of most Linux desktop distributions and many embedded distributions. Its memory allocator is used in everything from starting threads to handling I/O. Learn how to leverage this extensive attack surface through various heap exploitation techniques, ranging from the original “Unsafe Unlink” to the elegant overflow-to-shell technique known as the “House of Orange”.
In this hands-on course, you will alternate between learning new techniques and developing your own exploits based on what you have learned. You will use the pwntools and pwndbg frameworks to spawn shells from vulnerable practice binaries, and take on challenges designed to test your understanding and practical skills.
What you’ll learn
- Scripting exploits with pwntools
- Introspecting the heap with pwndbg
- The House of Force technique
- The Fastbin Dup technique
- The Unsafe Unlink technique
- The Safe Unlink technique
- The House of Orange technique
- Using one-gadgets to drop a shell
- Leveraging a single-byte heap overflow to drop a shell
Who this course is for
- Exploit developers
- Capture The Flag (CTF) players
- Those wishing to learn more about exploit dev than just stack buffer overflows
- Anyone interested in weird machines
Specificatoin of Linux Heap Exploitation – Part 1
- Publisher : Udemy
- Teacher : Max Kamper
- Language : English
- Level : Intermediate
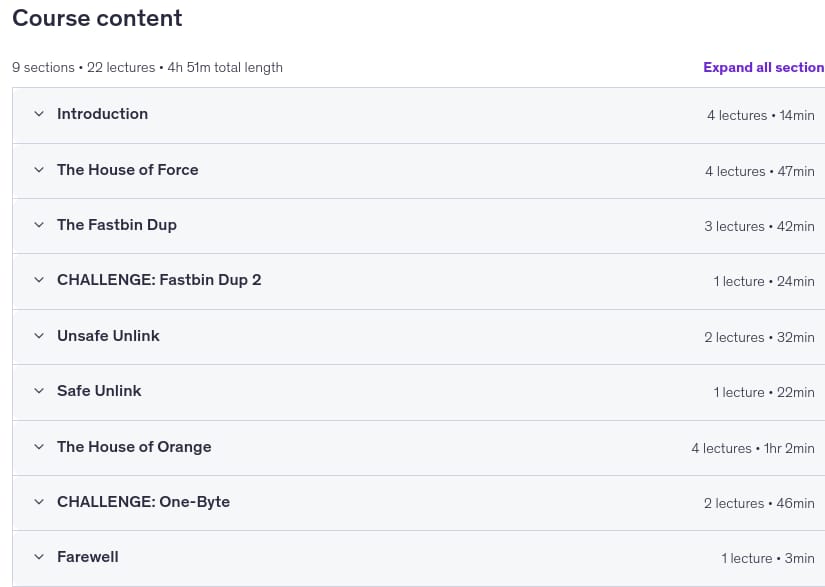
- Number of Course : 22
- Duration : 4 hours and 51 minutes
Content of Linux Heap Exploitation – Part 1
Requirements
- Familiarity with the Linux command line environment
- Basic debugging skills
- An x64 Linux VM or Host
Pictures
Sample Clip
Installation Guide
Extract the files and watch with your favorite player
Subtitle : English
Quality: 720
Download Links
Password file(s): www.downloadly.ir
File size
1.15 GB