
Description
“Hacking AI Agents: Hands-On LLM Red Teaming” is a training course focused on identifying vulnerabilities and security testing for Large Language Models (LLMs) and autonomous AI systems, published by the online learning platform Udemy. You will learn how AI agents function, understand their potential attack surfaces, and discover how attackers might exploit weaknesses in prompts, model behavior, tool integrations, and external data sources. The course covers key LLM security concepts, including prompt injection, jailbreaking, sensitive information disclosure, insecure tool usage, excessive agent permissions, and indirect prompt attacks. You will gain hands-on experience with red teaming methodologies, adversarial testing techniques, vulnerability assessment, and strategies for evaluating the reliability and security of AI-powered applications.
You will learn how to identify weaknesses within agentic workflows, assess risks associated with connected tools and APIs, and implement effective protective measures to enhance the resilience of AI systems. Whether you are an AI engineer, a cybersecurity specialist, a penetration tester, or a developer building LLM-based applications, this course will help you develop the practical skills needed to test, secure, and protect modern AI agents against emerging threats. Throughout this course, you will map the attack surface, execute prompt injections, bypass safety filters, construct attack chains, implement layered defenses, automate red teaming using tools such as Garak and PyRIT, and produce a red-team report aligned with OWASP and NIST standards. This journey provides a deep, practical understanding of how these concepts apply to real-world scenarios, preparing you to professionally secure AI systems.
What you will learn in Hacking AI Agents: Hands-On LLM Red Teaming:
- Map the attack surface of an LLM app or agent and scope an authorized engagement.
- Run direct and indirect prompt injection and reproduce a data leak on a live local target.
- Bypass safety filters with persona, encoding, multi-turn, and crescendo techniques.
- Chain injection, memo poisoning, and tool abuse into an unauthorized money-movement kill chain.
- Run extraction and poisoning attacks and write a detector for the poisoned data.
- and …
Course specifications
Publisher: Udemy
Instructors: Dr. Amar Massoud
Language: English
Level: Introductory to Advanced
Number of Lessons: 34
Duration: 1 hour and 23 minutes
Course topics
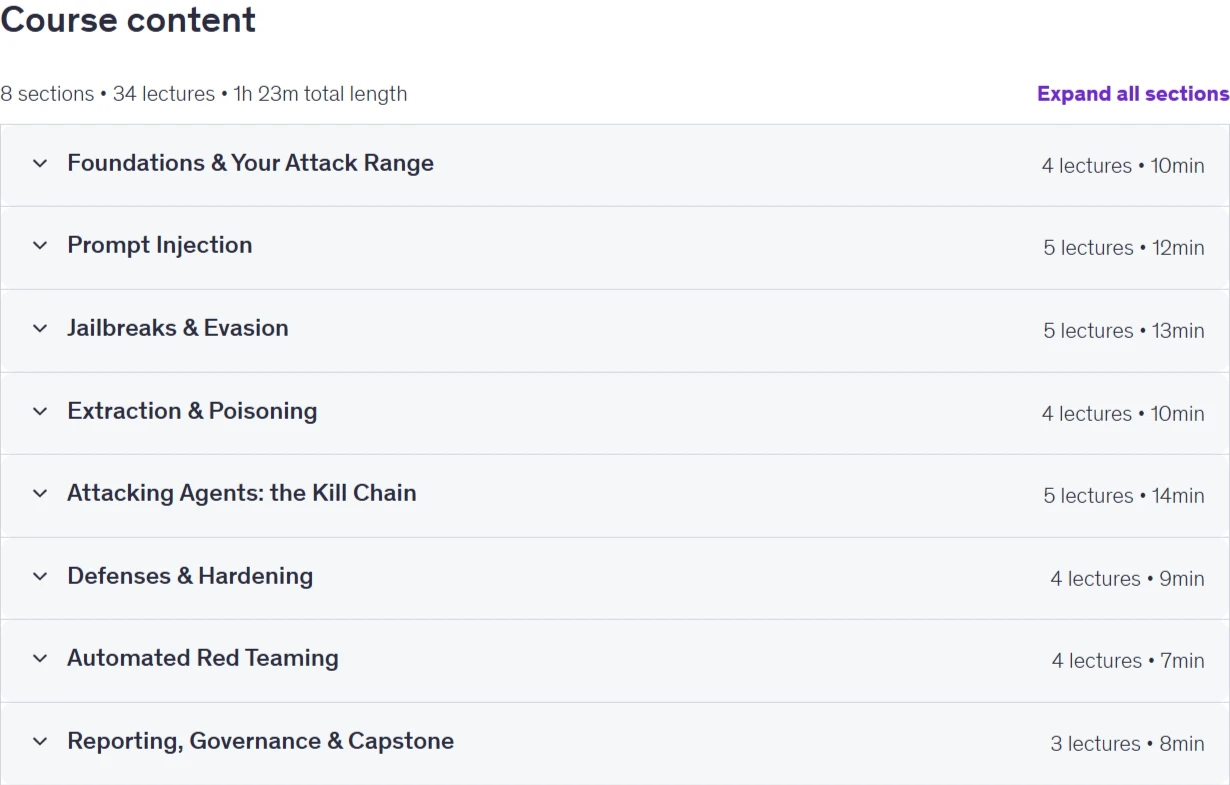
Hacking AI Agents: Hands-On LLM Red Teaming Prerequisites
A computer that can run a small local model (about 8 GB RAM recommended) and Python 3.11 or newer
Free software only: Ollama with a small local model; Docker is optional
Basic comfort with a terminal and reading short Python scripts
No prior AI security experience needed; general IT or security awareness helps
Pictures
Hacking AI Agents: Hands-On LLM Red Teaming introduction video
Installation guide
After Extract, watch with your favorite Player.
English subtitle
Quality: 1080p
Downloadly link
Rapidgator link
File password (s): www.downloadly.ir
Size
411 MB