

Descriptions
Cybersecurity Risk Management Frameworks Specialization, Cybersecurity Risk Management Frameworks Specialization is a 4-course series that develops a practical understanding of cybersecurity risk and the frameworks used to manage it in organizations. The specialization covers how to define cybersecurity risk and the threats that create it, the role of cybersecurity management in managing risk, the elements of a general risk management framework, and how to develop and administer a risk management effort. Learners also examine dominant risk management standards and frameworks, including guidance from NIST and the International Organization for Standardization, as well as the tools and approaches used to support organizational risk management. The program builds from cybersecurity foundations and general risk management concepts to the implementation of a risk management framework and cybersecurity governance.
What you’ll learn
- Define key concepts and terminology in cybersecurity and identify the threats that create cybersecurity risk.
- Describe the role and responsibilities of cybersecurity management in an organization’s risk management effort.
- Explain cybersecurity risk and how an organization develops and manages a program to address it.
- Develop a general risk management framework to guide an organization’s risk management efforts.
- Perform risk assessment to identify risks to an organization’s information assets and discuss strategies for reducing those risks to an acceptable level.
- Explain dominant risk management standards and frameworks, including NIST and ISO approaches, and identify tools that support organizational risk management.
- Apply a risk management framework to a sample organization by identifying, classifying, and prioritizing organizational assets and the threats to those assets.
- Understand the role of cybersecurity governance and the strategic responsibilities of the CISO in overseeing an organization’s cybersecurity program.
Who this course is for
- Beginners who want to build a foundation in cybersecurity risk management and understand the threats that create cybersecurity risk.
- Information systems and cybersecurity learners who want to understand risk assessment, risk treatment, risk mitigation, and organizational risk management.
- Professionals who want to learn about NIST, ISO/IEC 27001, risk management frameworks, security controls, and other standards and tools used to support risk management.
- Learners who want to apply a risk management framework to organizational assets and threats and understand cybersecurity governance and the role of the CISO.
Specificatoin of Cybersecurity Risk Management Frameworks Specialization
- Publisher : Coursera
- Teacher : Herbert J. Mattord, Ph.D., CISM, CISSP, CDP
- Language : English
- Level : Beginner
- Number of Course : 4
- Duration : 4 weeks to complete at 10 hours a week
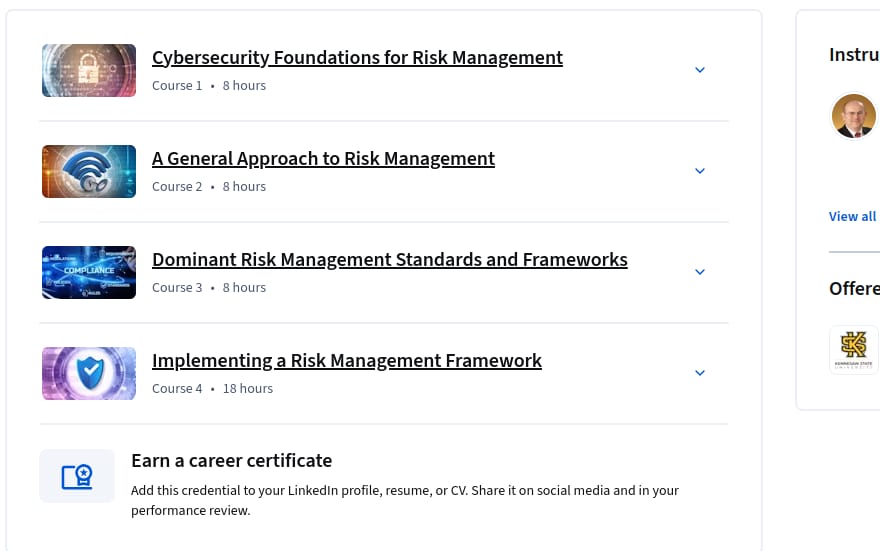
Content of Cybersecurity Risk Management Frameworks Specialization
Requirements
- We recommend learners have an understanding of computers and applications as well as prior work experience in cybersecurity or risk management.
Pictures
Sample Clip
Installation Guide
Extract the files and watch with your favorite player
Subtitle : English
Quality: 720p
Download Links
Course 1 – Cybersecurity Foundations for Risk Management
Course 2 – A General Approach to Risk Management
Course 3 – Dominant Risk Management Standards and Frameworks
Course 4 – Implementing a Risk Management Framework
Password file(s): www.downloadly.ir
File size
653 MB