

Description
Wireshark for SOC Analyst & AI-Powered Analysis is a course on how to use Wireshark for network traffic analysis, threat detection, and SOC investigations using AI-powered analysis, published by Udemy Online Academy. This course is suitable for aspiring SOC analysts, cybersecurity professionals, network advocates, and security enthusiasts, and begins with the fundamentals of networking and cybersecurity before progressing to packet capture, filtering, TCP/IP analysis, and protocol-level analysis, combining traditional analyst skills with a modern AI-powered workflow. Learners begin by establishing their understanding of core networking and cybersecurity concepts, ensuring they understand the underlying protocols and traffic behavior before delving into Wireshark itself. The course then covers packet capture and filtering, teaching learners how to use both display and capture filters to isolate relevant threats within large, crowded packet captures, rather than manually scanning everything. The main part of the course focuses on analyzing real PCAP files, giving learners first-hand experience identifying suspicious traffic patterns, the way a real SOC analyst would, rather than relying on simplified textbook examples.
Learners examine protocol-level activity across TCP, UDP, DNS, HTTP, HTTPS, SMB, and FTP, along with ICMP traffic, building a broad and practical understanding of the differences between legitimate and malicious traffic at each layer. Specific attack patterns are directly covered, and learners learn to identify indicators such as port scans, brute-force attempts, DNS tunneling, and malware command-and-control communications within captured traffic. These patterns form the practical backbone of the real work of SOC investigation. What sets this course apart is its integration with AI-assisted analysis: Learners connect Claude AI to Wireshark via an MCP server, allowing them to examine traffic using natural language queries, rather than relying solely on manual filter syntax. This combines traditional packet analysis skills with a modern workflow that accelerates analysis without replacing analyst judgment. By the end of the course, learners will be ready to perform real-world network traffic analysis and threat detection, augmented with the practical help of AI.
What you will learn in Wireshark for SOC Analyst & AI-Powered Analysis:
- Analyze real PCAP files and identify suspicious traffic patterns like a SOC analyst
- Apply display filters and capture filters to isolate threats in large packet captures
- Investigate protocol-level activity across TCP, UDP, DNS, HTTP, HTTPS, SMB and FTP
- Connect Claude AI to Wireshark via MCP server and investigate traffic using plain English
- and …
Course specifications
Publisher: Udemy
Instructors: Rajneesh Gupta and Jaimin Pathak
Language: English
Level: Introductory to Advanced
Number of Lessons: 43
Duration: 4h 10m
Course topics
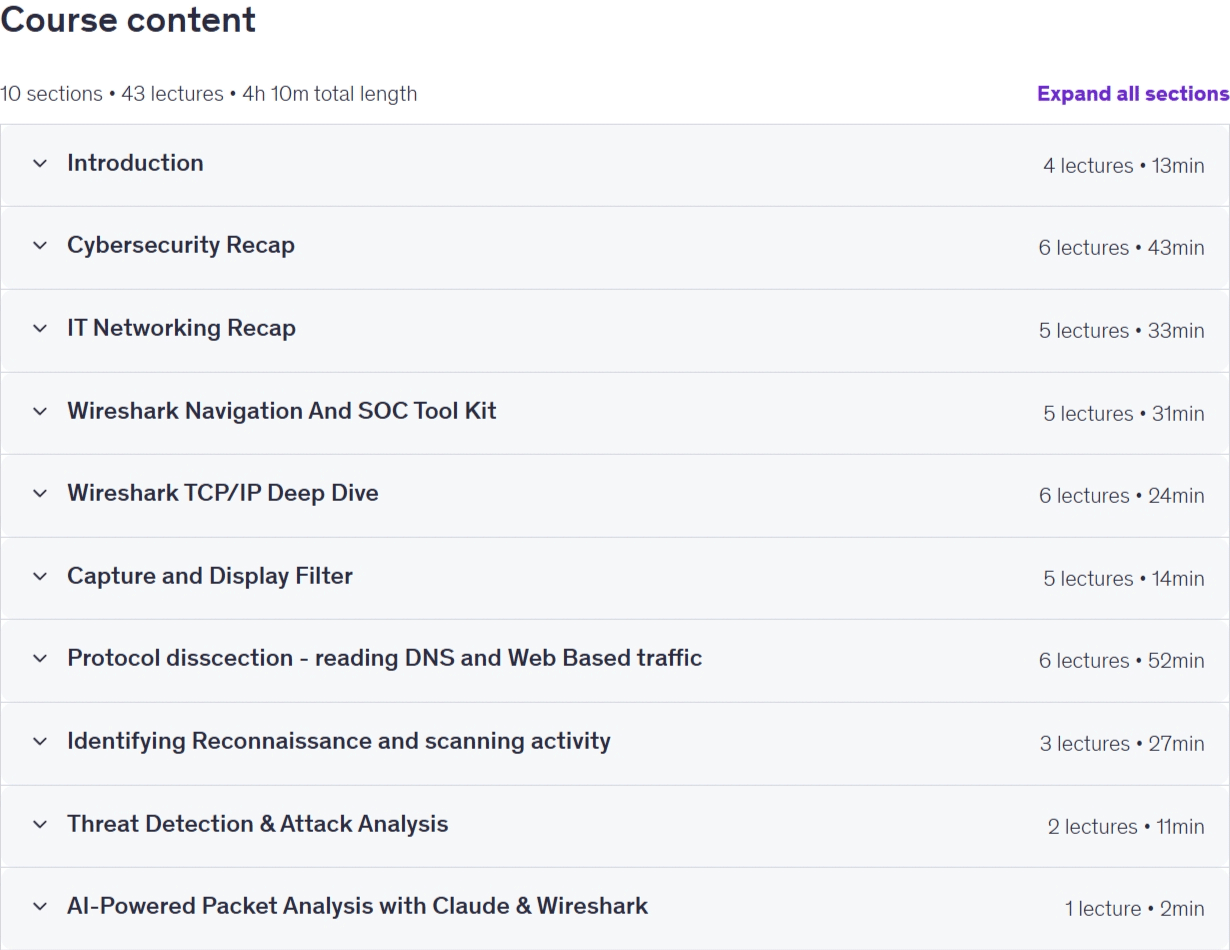
Wireshark for SOC Analyst & AI-Powered Analysis Prerequisites
Basic understanding of networking concepts like IP addresses, ports and protocols — no deep expertise needed
A Windows, Mac or Linux computer to install Wireshark — all software used is free and open source
Pictures
Wireshark for SOC Analyst & AI-Powered Analysis introduction video
Installation guide
After Extract, watch with your favorite Player.
Subtitle: None
Quality: 1080p
Downloadly link
Rapidgator link
File password (s): www.downloadly.ir
Size
4.1 GB