
Description
Building a Reflective DLL Loader in C++. This course provides an in-depth look at reflective DLL loading techniques in C++, with a focus on Windows internals, reverse engineering, and security analysis. This course provides an in-depth look at reflective loading techniques in C++ from the perspective of Windows internals, reverse engineering, and cybersecurity defense research. Participants will learn how to load and execute executable modules directly from memory without the need for a standard operating system loader, while gaining a deep understanding of the underlying mechanisms that enable these techniques. This course covers key concepts including the executable file format (PE Format), process memory structure, relocations, import resolution, memory protection, and related Windows APIs. Through guided demonstrations, code analysis, and hands-on lab exercises in an isolated environment, learners will explore how reflective loading implementations work and how these behaviors emerge during malware analysis and incident response processes. The training focuses equally on identifying signs of in-memory execution, understanding how modern security products detect these techniques, and applying defensive methods to inspect and hunt for threats. By the end of the course, participants will be able to describe reflective loading architecture, analyze implementations using debugging and reverse engineering tools, identify forensic traces associated with in-memory code, and enhance their ability to detect, analyze, and respond to complex threats while adhering to ethical, legal, and responsible security research practices. This course is highly applicable and useful for penetration testers, red team members, malware analysts, and cybersecurity researchers.
What you will learn
- Navigating the PEB Structure: Learn how to navigate and examine the structure of the Process Environment Block.
- Understanding the PE format: Complete learning of the format and structure of executable files (Portable Executable).
- DLL reflective loading process: Learn the complete steps and process of loading DLL reflectively into memory.
- Building a Code Injector: How to build an injector to inject Reflective DLLs into processes.
This course is suitable for people who:
- Penetration Testing Specialists: Penetration testers who want to learn advanced code injection techniques.
- Red Teamers: Red Teamers are experts in simulating complex attacks in enterprise environments.
- Malware developers: People who seek to understand the mechanisms of creating memory-resident code.
- Malware analysts: Specialists who want to identify and analyze the behaviors of memory-resident malware.
Course details: Building a Reflective DLL Loader in C++
- Publisher: Udemy
- Instructor: Naga Sai Nikhil
- Training level: Beginner to advanced
- Training duration: 3 hours and 33 minutes
- Number of lessons: 20
Course topics
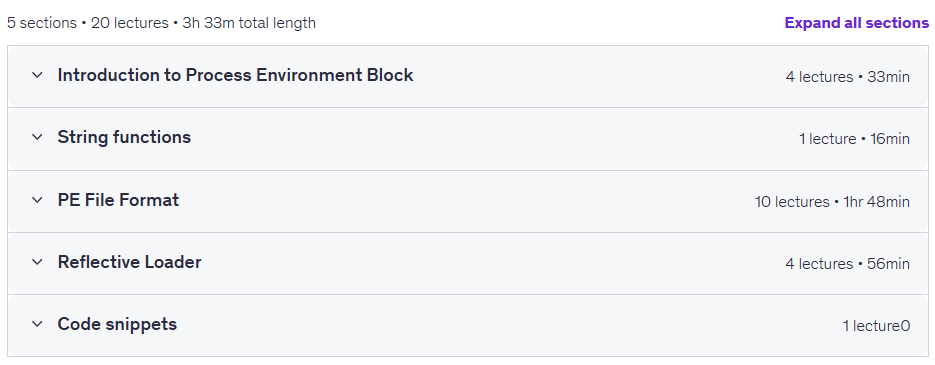
Prerequisites for the Building a Reflective DLL Loader in C++ course
- Basics of C or C++ programming is required
- Enthusiasm
Course images
Sample course video
Installation Guide
After Extract, view with your favorite player.
Subtitles: None
Quality: 2160p
Download link
Rapidgator link
File(s) password: www.downloadly.ir
File size
6.1 GB